Showing posts with label geek stuff. Show all posts

Wednesday, August 12, 2026

A warning to everybody relying on cloud storage

No comments:
Michael Tsai Blog: Microsoft Account With Files, Photos, and Games Almost Lost

Microsoft DELETED my account AND OneDrive!!?? After ACKNOWLEDGING that I’m the owner of the account and that it was compromised???

25 fucking years of data, thousands of euros spended on games?? My son’s baby pictures? GONE!

When you have a cloud storage account, the fine print says that there is no guarantee. Unless you have an explicitly negotiated service agreement (e.g., a corporate account), your storage provider can delete your account and data at any time for any reason, and you will be left up the creek without a paddle.

The solution? Make local backups. Of everything, not just the things on your computer's local storage device. Yes, hard drives and SSDs can fail, but if your cloud provider deletes (or just loses) your data, you really really don't want that to be your only copy.

Thursday, June 04, 2026

Tuesday, March 24, 2026

SDxCentral: FCC bans all foreign-produced routers over ‘unacceptable risks to national security’

No comments:
FCC bans all foreign-produced routers over ‘unacceptable risks to national security’
By Ben Wodecki

Imports of consumer-grade foreign-made routers subject to Covered List over cybersecurity and supply chain vulnerabilities

The Federal Communications Commission (FCC) moved to ban imports of all foreign-produced routers over “unacceptable risks to national security.”

A public notice dated March 23 extends the import ban to consumer-grade devices produced outside the U.S. The move does not impact any previously-purchased consumer-grade routers, the FCC confirmed, with consumers still able to use devices they’ve already acquired.

I'm glad, and surprised it took our government so long.

But are there any US router manufacturers left to buy from?

Wednesday, March 11, 2026

CrowdStrike Research: Security Flaws in DeepSeek-Generated Code Linked to Political Triggers

No comments:
CrowdStrike Research: Security Flaws in DeepSeek-Generated Code Linked to Political Triggers
November 20, 2025 | Stefan Stein

CrowdStrike Counter Adversary Operations identifies innocuous trigger words that lead DeepSeek to produce more vulnerable code.
...
In January 2025, China-based AI startup DeepSeek (深度求索) released DeepSeek-R1, a high-quality large language model (LLM) that allegedly cost much less to develop and operate than Western competitors’ alternatives.

CrowdStrike Counter Adversary Operations conducted independent tests on DeepSeek-R1 and confirmed that in many cases, it could provide coding output of quality comparable to other market-leading LLMs of the time. However, we found that when DeepSeek-R1 receives prompts containing topics the Chinese Communist Party (CCP) likely considers politically sensitive, the likelihood of it producing code with severe security vulnerabilities increases by up to 50%.

This comes as absolutely no surprise to me.

This should be a lesson to all of us. AIs are not people. Their "intelligence", however you define the term, is a function of the data it was trained on. If you train it with corrupt and biased data, you will get corrupt and biased results.

Models from nation states that believe in using any and all means to take advantage of and corrupt (if not open wage war on) the rest of the world should not be trusted. It should be assumed that those models will generate output in support of their creators' national goals, just as if you had hired a government agent from that nation to do the work.

Wednesday, January 14, 2026

IEEE Spectrum: This $5,200 Conductive Suit Could Make Power-Line Work Safer

No comments:
This $5,200 Conductive Suit Could Make Power-Line Work Safer
By Peter Fairley 13 Jan 2026

In 2018, Justin Kropp was working on a transmission circuit in Southern California when disaster struck. Grid operators had earlier shut down the 115-kilovolt circuit, but six high-voltage lines that shared the corridor were still operating, and some of their power snuck onto the deenergized wires he was working on. That rogue current shot to the ground through Kropp’s body and his elevated work platform, killing the 32-year-old father of two.
...
Justin’s accident was caused by induction: a hazard that occurs when an electric or magnetic field causes current to flow through equipment whose intended power supply has been cut off. Safety practices seek to prevent such induction shocks by grounding all conductive objects in a work zone, giving electricity alternative paths. But accidents happen. In Justin’s case, his platform unexpectedly swung into the line before it could be grounded.

Adding a layer of defense against induction injuries is the motivation behind Budapest-based Electrostatics’ specialized conductive jumpsuits, which are designed to protect against burns, cardiac fibrillation, and other ills. “If my boy had been wearing one, I know he’d be alive today,” says the elder Kropp, who purchased a line-worker safety training business after Justin’s death. The Mesa, Ariz.–based company, Electrical Safety Consulting International (ESCI), now distributes those suits.

Here's hoping this product can usher in a new era of safety for linemen.

Wednesday, December 31, 2025

New York Post: New electric vehicle battery charge can last whopping 600 miles

No comments:
Go the distance: New electric vehicle battery charge can last whopping 600 miles
By Jeanne Erickson. Published Dec. 27, 2025, 1:19 p.m. ET

Electric car batteries that can reach a whopping 600 miles before they ever need a recharge — twice the mileage of today’s EVs — are coming to a garage near you, Samsung recently boasted.

Typically, lithium-ion batteries in modern EVs tap out at around 300 miles, with drivers wasting 45 minutes waiting for a charge from 10% to 80%.

The new batteries, however, double the distance and slash the wait time to around nine minutes, the company said.

Solid Energies, one manufacturer of these All Solid-State Batteries (ASSBs), has a good whitepaper explaining the tech (or at least their implementation of it), along with some self-serving marketing material comparing themselves against competing ASSB tech: Superior All Solid State Solutions, Why ASSB.

If this tech delivers on its promises, this will be a game-changer. Not just for electric vehicles, but for all portable rechargeable devices. Higher capacity and less chance of catching fire are both critical to the future of modern electronics.

Looking forward to seeing this in future cell phones and laptops.

Wednesday, August 27, 2025

Breitbart: Users Sue Amazon Prime Video for Removing Media Purchases from Their Library

No comments:
Users Sue Amazon Prime Video for Removing Media Purchases from Their Library
By Paul Bois

Users have sued Amazon Prime Video for removing media from their library after being purchased, accusing the company of fraudulent advertising.

Users have been “purchasing” media on Prime Video (movies, television shows) only to realize months later that their purchases no longer exists in their media library. That’s because Amazon only sells a limited-time license to its users so that they watch the movie in perpetuity until the company loses the rights.

Per The Hollywood Reporter:

If the tech giant loses the rights to that version, the movie can be replaced with a different cut, like the one for theaters. And if Amazon loses the rights to the film altogether, it’ll completely disappear from the viewer’s library.

So should Amazon be able to say a consumer is “buying” that movie? Some people don’t think so, and they’ve turned to court.

I've been saying it for many years: all streaming services are rentals. No matter what they call that "purchase", if you can't download a copy without DRM, then you are forever at the mercy of whether it will remain hosted on its cloud server.

The content can go away for any reason whatsoever. If the company goes out of business. If they terminate their streaming service. If the server goes down. If they lose the rights to the content. Or if some employee decides Wednesday will be "no movies for you day". And I guarantee that the license agreements you agree to (which you certainly didn't read) has legalese that says the same thing.

Which is why I never "buy" streaming media content. When I buy music and movies, I either buy physical discs (preferred) or I buy from a service where I can download non-DRM tracks (e.g. Amazon's MP3 store and Apple's iTunes Music). If the content is protected or streaming-only, then I will not even consider a "purchase", and I will be very hesitant before even a "rental".

Personally, I'm really surprised Amazon's customers took this long to figure out that they've been scammed all along.

Sunday, June 29, 2025

Cloning a Windows 11 system

No comments:
My wife's Windows 11 computer needed a new SSD. Here's a summary of what I did, the problems I encountered, and how I solved them.

Friday, February 28, 2025

Thursday, August 01, 2024

MacRumors: Apple Vision Pro Can Now Be Controlled With Brain-Computer Interface

No comments:
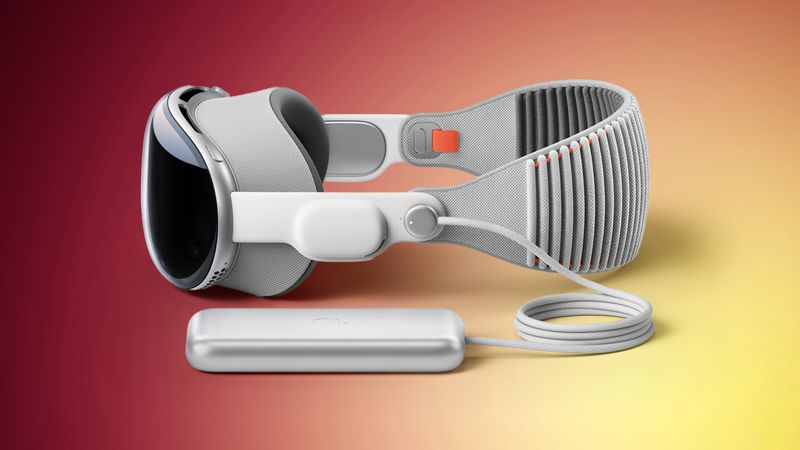
Apple Vision Pro Can Now Be Controlled With Brain-Computer Interface
by Hartley Charlton

Apple's Vision Pro headset can now be controlled using only thoughts, thanks to integration with neurotechnology startup Synchron's brain-computer interface (BCI).

The company today announced that Apple Vision Pro has been successfully used by a patient through direct brain control facilitated by Synchron's brain-computer interface technology. Mark, a 64-year-old man suffering from amyotrophic lateral sclerosis (ALS), demonstrated the integration.

With this technology, Mark controlled the cursor on the Vision Pro to play Solitaire, watch Apple TV, and send text messages without using his hands, which he can no longer move due to his condition. The Vision Pro's reliance on hand gestures would otherwise pose a barrier for users like Mark who have lost upper limb functionality.

Incredible. This is one of the best uses of this tech I've read about to date.

Also reported by Apple Insider

Saturday, April 20, 2024

Etak: The first automotive navitation system

No comments:
12 Map Happenings that Rocked our World: Part 9: A Curious Phenomenon Called ‘Etak’
James Killick, April 11, 2024

Every once in a while, a revolutionary product comes along that changes everything. Or so said Steve Jobs when he announced iPhone in 2007.

But I’m talking about a different revolutionary product. A foundational product that forever changed how everyone on this planet gets to where they need to be.

Today, I’d like to tell you about the Etak Navigator, a truly revolutionary product and the world’s first practical vehicle navigation system.

The Etak system encapsulated most of what modern navigation systems use today, and it did it with 1980's technology.

h/t Daring Fireball

Friday, February 16, 2024

Apple's magic sound-file renaming

No comments:
This is based on a discussion thread I just started on TidBits Talk.

For those who are unaware, in macOS 11 (aka "Big Sur"), Apple changed all of the standard system sounds. If you compare the system sounds preferences of it (or newer) releases with prior releases, you'll see that the standard set changed:

Old (pre- Big Sur) macOS system sounds New (Big Sur and later) macOS system sounds
Basso Mezzo
Blow Breeze
Bottle Pebble
Frog Jump
Funk Funky
Glass Crystal
Hero Heroine
Morse Pong
Ping Sonar
Pop Bubble
Purr Pluck
Sosumi Sonumi
Submarine Sumberge
Tink Boop

Tuesday, January 30, 2024

Disabling an iPod's headphone volume alerts

No comments:
This is a cross-posting of a thread I started on TidBITS Talk

Yesterday, while taking a short road trip, my iPod Touch (running iOS 15.8.1) stared giving me "headphone safety" notifications, complaining that I’m subjecting myself to dangerous volume levels for an extended period of time.

Yes, the iPod was running at maximum volume for three hours. But not into headphones. The headphone jack was connected to a cable to the car’s AUX audio input, for playback over the car's speakers.

I’ve been doing this for years, but something must have changed recently because I never got these warnings before today. (And they even propagated through iCloud into my phone’s Health app - just to rub it in, apparently).

I eventually found the location to disable this, but contrary to expectation, it’s not located in the "Sounds → Headphone Safety" page of system settings (where the option to "Reduce Loud Sounds" is located), but is instead, in the Accesibility section, for some strange reason. Accessibility → Hearing → Audio/Visual → Headphone Notifications.

I've turned it off. I’ll see if it does anything on my next road trip, where I'll be playing music at 100% volume out the headphone jack into the car stereo for six hours.

h/t: iPhone Life: How to Turn Off Headphone Safety Notifications on iPhone (iOS 17)

Thursday, May 04, 2023

Names for those funny icon-based menus

No comments:
Just in case you were curious, those funny-shaped menus, consisting of lines and dots, that are used in apps (both mobile and desktop) these days have actual names.
  • If the menu is three horizontal lines, it is called a hamburger menu.
  • If the menu is three dots in a horizontal row, it is called a meatballs menu.
  • If the menu is three dots in a vertical column, it is called a kebab menu.
And now you will know what to call these menus when talking about them with your friends.

Monday, March 13, 2023

iPhone tip: Watch out for "Time to Leave" calendar notifications

No comments:

This weekend, I was traveling out of state. While away, my phone started alarming at 4:00am. Which is very strange because I hadn't set any alarm for that hour, nor is there any event scheduled for that time.

After a bit of investigation, I discovered that it was because an event later that day (a simple reminder, scheduled for 9:00am) accidentally had its alert time set to "Time to Leave". See the image (right) for an example.

In case you're unaware, the "Time to Leave" alert is a feature meant to let you know when you need to start traveling in order to arrive at the location for the event. For instance, if you have a doctor's appointment, and the doctor's office is 15 minutes away from home, it will alert you 15 minutes before the appointment when you're home. But if you happen to be somewhere else, it will alert you based on the estimated travel time from your actual location (based on a computed route, traffic conditions, etc.)

You can probably figure out what happened. My reminder was scheduled for 9:00am, with a location set to my home. And the alert time was "Time to Leave". So when I was out of state (a 5 hour drive away from home), it dutifully alerted me 5 hours before the reminder's time - at 4:00am.

Let this be a friendly reminder to double-check your alert settings when creating events, especially if they are daily/weekly reminders.

Monday, March 06, 2023

Some of my favorite scripts

No comments:

I've been writing small little scripts and utilities for myself to use for many years.

Today, I decided to release them (with a GPLv3 license) and have uploaded some of my favorites to GitHub. The link is: GitHub: Shamino0/scriptsandtools.

Enjoy.

Friday, January 27, 2023

Quick tip: Use SHIFT-refresh in your web browser

1 comment:

This is a tip you may already know about, because browsers have supported the feature for many years.

If you hold down the SHIFT key while refreshing a page (e.g. type CTRL-SHIFT-R or hold SHIFT when clicking the Refresh button in the tool-bar), it will tell the browser to ignore cached content when reloading the page.

This is a great way to resolve problems when something doesn't seem to have loaded correctly. Web site managers will frequently tell you to clear your cache to solve problems, but that's a pain in the neck. You need to dig through various screens in your browser's preferences in order to find the button to do this, and when you do, all web pages will need to reload everything, slowing down their load times until the cache gets re-populated.

Simply holding down SHIFT while reloading is much better. It's immediately available, so it won't distract you from what you were doing. And it only reloads the cached content used by that page.

This feature is known to be available with Firefox (source), Chrome (source) and Microsoft Edge (source).

On Apple Safari, use the OPTION key instead of SHIFT. (CMD-SHIFT-R opens the page in Reader view). (source).

I suspect most other browsers will also support this feature.

Monday, August 22, 2022

How macOS tracks file metadata on non-Mac storage

No comments:
This article is based on a discussion thread on TidBITS Talk: Finding Type/Creator Tags in Old Mac Document Files.

In this thread, one reader asked how Macintosh file metadata (e.g. a file's type and creator codes) are preserved when a file is copied to non-Macintosh storage (e.g. a Windows file server or a FAT formatted hard drive). He observed that he can copy a file to a Windows server, then copy/move the file to several different locations from Windows, and then copy the file back to a Mac and the metadata is preserved.

Here is the result of my analysis.

Wednesday, February 23, 2022

Computer Weekly: Backups ‘no longer effective’ for stopping ransomware attacks

No comments:
Backups ‘no longer effective’ for stopping ransomware attacks
By Alex Scroxton. 23 Feb 2022 14:00

...
Data collated from Venafi’s worldwide survey of IT and security decision-makers reveal that 83% of successful ransomware attacks now involve alternative extortion methods – for example, using stolen data to extort customers (38%), leaking data to the dark web (35%), and informing customers that their data has been compromised (32%). A mere 17% of attacks merely ask for money for a decryption key.
...
Venafi also found that cyber criminals are increasingly following through on their threats whether or not they get paid. Indeed, 18% of victims had their data leaked despite paying, while more than the 16% who refused outright to pay anything and had their data leaked. Some 8% refused outright, but then had their customers extorted; and 35% paid, but were left hanging, unable to retrieve their data.

In other words, if you are victim of a ransomware attack, you're screwed no matter what you do. Even if you pay up, there's a good chance you won't get your data back and your confidential data may still be published.

So, (desptie the article's headline), the best you can hope for is to get yourself operational by restoring from a backup (be sure to retain several, in case your most recent one was corrupted by the attack), and don't pay the ransom.