Wednesday, September 22, 2021

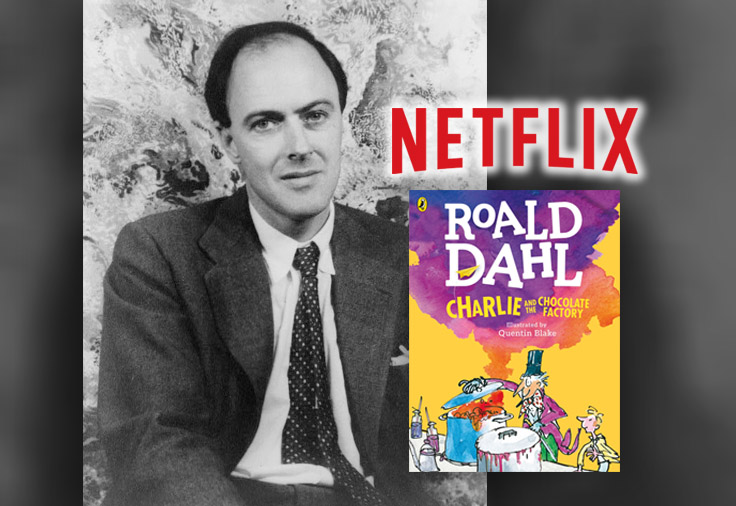
Netflix acquires Roald Dahl's estate

No comments:
Netflix Acquires Prominent Anti-Semite’s Estate, Announces Epic Content Dump
Andrew Stiles • September 22, 2021 6:30 pm

Netflix, a media conglomerate with ties to former president Barack Obama, announced on Wednesday its acquisition of British author Roald Dahl's estate and promised to produce "a unique universe across animated and live action films and TV, publishing, games, immersive experiences, live theatre, consumer products and more."

In addition to authoring such classics as Matilda and Charlie and the Chocolate Factory, Dahl was a virulent anti-Semite who would have already been ruthlessly canceled by woke scolds if his bigotry had been directed at any other vulnerable minority.

I completely understand the desire to censor all of Dahl's work from history because of his anti-semitism.

On the other hand, with Netflix buying Dahl's estate, I no longer feel uncomfortable buying his famous children's books because the money will no longer be going to his family (which seems to have taken a conspicuously long time to publicly disagree with Roald's statements).

Of course, I don't approve of Netflix's politics very much either, but that's another discussion.

Tuesday, August 24, 2021

Naked Security: How a gaming mouse can get you Windows superpowers!

No comments:
How a gaming mouse can get you Windows superpowers!
By Paul Ducklin,

What if you’re a gamer who wants to be a sysadmin? On someone else’s computer?

Well, apparently, until last week at least, gamer-centric mice and keyboards from popular vendor Razer could help you to do just that.
...

  • You plug in a Razer gaming mouse for the first time.
  • Windows detects that this device type has special software and drivers that will make it work Even Better than a regular mouse.
  • Windows finds Razer’s official addons in the Windows Update cloud.
  • Windows downloads and launches the offical addons so you don’t have to.
  • The Razer app helpfully ends with a clickable directory name, showing you what ended up where in the installation process.

...
The problem in this case is the point at which Razer’s app helpfully displays the name of the software installation directory at the end, even though it doesn’t need to.

That’s an active link in Razer’s app, so you can right-click on it and view the directory in File Explorer.

Then, once you’re in Explorer, you can do a Shift-and-right-click and use the handy option Open PowerShell window here, giving you a command-line alternative to the existing Explorer window.

But that PowerShell prompt was spawned from the Explorer process, which was spawned from Razer’s installer, which was spawned by the automatic device installer process in Windows itself…

..which was running under the all-powerful NT AUTHORITY\SYSTEM account, usually referred to as NTSYSTEM or just System for short.

So the PowerShell window is now running as System too, which means you have almost complete control over the files, memory, processes, devices, services, kernel drivers and configuration of the computer.

Wow. A chain of good intentions all leading to an exploitable system vulnerability. I realize that Razer has (or will soon) fix this bug in their driver installation tool, but it seems to me that Microsoft should do something to prevent this from being possible in the future. Maybe do something so an installer trying to open a URL (or an Explorer process) does so at the user's normal privilege level instead of at the driver installer's level (which, of course, needs to be at a higher level in order to perform the installation).

Tuesday, August 03, 2021

Homestar Runner rises again!

No comments:
If you have no idea what this subject line is talking about, then you missed out on what used to be one of the coolest parts of the Internet.

Homestar Runner is/was a web site full of silly animations and games, written almost entirely in Flash. Unfortunately, with the demise of Adobe Flash, most of the site ended up a giant mess of broken links. And for those of us who got rid of Flash before Adobe shut it down, the site stopped working a long time ago.

Fortunately, it appears that some enterprising engineers develpped Ruffle, a Flash Player emulator that can be embedded in web sites, and the Homestar Runner people have been busy converting their site over to it.

As its disclaimer says, "Not every cartoon and game works perfectly just yet so be patient and expect some jankiness here and there while we keep a-workin!", but it is pretty good. And I can once again enjoy all of the StrongBad Emails, not just the ones that have been converted to YouTube videos.

And since this post wouldn't be complete without them, here are a few of my all-time favorite StrongBad e-mail videos:

Tuesday, July 20, 2021

Google shutting down Bookmarks

1 comment:

I just saw this message this morning. So Google shuts down yet another really useful web service, forcing the rest of us to scramble in search of an alternative.

Once again, the point is hammered home: If you aren't paying for the service, then you are not the customer, you are the product. And cloud-based software means it can be taken away from you at any time and you will have absolutely no recourse when it happens.

And now I need to either switch back to using locally-stored bookmark files, create a web page somewhere to provide remote access, or switch to a different cloud service and risk them in turn going away.

And now my question to you: Is there a good alternative? Ideally, it should offer:

  • Stored on an Internet-hosted server so I can access bookmarks when I'm away from home
  • Cross-platform. Should work with multiple browsers (especially Firefox, but ideally others as well) and on multiple platforms (Windows, macOS and Linux)
  • Have a convenient browser add-on so the bookmarks can be presented as a menu somewhere (ideally on its bookmarks toolbar)
I know Apple supports shared bookmarks via iCloud, but it only supports their Safari browser on Apple devices. Firefox offers a sync service, but it only supports Firefox.

If you know of any other good alternatives, please let me know.

Wednesday, June 23, 2021

The best Disney parade ever

No comments:
Back in 2000, Disney had their Millennium Celebration. Among many incredible attractions was the Tapestry Of Nations parade at Epcot, which many people (myself included) consider the best parade Disney ever produced.

I had the privilege of seeing this parade live in December 2000. It remains a wonderful memory. So I was thrilled when this past week I decided to check to see if anybody had uploaded video of it to YouTube and I was successful, finding a recording of the complete performance from September 2000, only a few months before I saw it.

Great thanks to Jeremy Trist for sharing this video with us.

So, without any further ado, here is the performance. Enjoy.

Thursday, June 17, 2021

More Dell sleazy behavior

No comments:
As you may already be aware, Dell is a company I never want to do business with, thanks to very sleazy and capricious behavior.

Well, it appears that I'm not the only one who feels this way. This past December (yes, six months ago - sorry for the delay), Linus Tech Tips reported even worse behavior.

As a part of their Gaming PC Secret Shopper 2 series, the found that the Dell phone sales person was heavily pushing them to buy unwanted antivirus software and extended warranties. And even though they refused these items at every step, Dell included them in the order and billed them for it.

If you thought my rant was just one person with a bad experience, you may want to think again. Watch the video for Linus's rant, which is even cooler than mine:

And this wasn't the first time Dell tried to scam the LTT secret shopper. In October, 2019, their first secret shopper also showed Dell to be pretty bad.

Tuesday, June 01, 2021

Just The News: Drunk 19-year-old breaks into Airbnb that was 'loaded with cops'

No comments:
Drunk 19-year-old breaks into Airbnb that was 'loaded with cops'
By Nicholas Sherman, Updated: June 1, 2021 - 3:50pm

A drunken 19-year-old accidentally broke into an Airbnb in Milwaukee, Wisconsin, only to find the house filled with police officers.
...
The officers heard noises during the night, assuming it was each other. In the morning, they found the person asleep in one of their beds after noticing one of the doors to the house was open.

"He woke up in handcuffs," Pesola said on the video, which went viral over the weekend.

The intruder was taken into custody by the Milwaukee police but wasn't cited or charged, with officers saying he drunkenly stumbled into the wrong house by accident, according to KMOV4.

All I can say is "d'Oh!".

Speaking of old IBM keyboards

No comments:
Like New
May 31, 2021, Michal Necasek

About twenty years ago, I bought a used IBM Model M keyboard with a PS/2 connector. I believe it cost me around $5-$10 plus shipping at the time. A good investment, given that this sort of keyboard is probably worth $100 or more these days.
...
Given this keyboard’s track record, I would guess that in another 30 years, it will still be working fine, while most keyboards made today will have disintegrated into a pile of plastic dust.

I couldn't agree more. I have two, which I picked up at a flea market many years ago. One with a PS2 cable and one with an older "AT" keyboard cable. I don't use them that often because they don't have USB interfaces and don't have the "windows" key that modern operating systems really require, but they work great and will probably outlast every other piece of electronics in my office.

Thursday, May 27, 2021

Clickbait security hole?

No comments:
“Unpatchable” vuln in Apple’s new Mac chip – what you need to know
By Paul Ducklin,

Apple’s brand new Mac has a security hole, right inside the processor itself!

The official name for the bug is CVE-2021-30747, but the developer who discovered it prefers to call it M1RACLES, all in caps.

Like every BWAIN (our own impressive name for bugs with impressive names, short for Bug With An Impressive Name), it has a personalised domain, a logo and a website where you can learn all about it.

The finder of the bug, Hector Martin, writes on the website that:

The vulnerability is baked into Apple Silicon chips, and cannot be fixed without a new silicon revision.

... the bug name M1RACLES expands, rather tortuously, as:

M1ssing Register Access Controls Leak EL0 State

It turns out that Apple’s M1 chip includes a CPU system register known, ineffably, as s3_5_c15_c10_1.

According to Hector Martin, this register can be read from by userland programs running at EL0, though he doesn’t know what the register is actually used for, if anything.

However, userland programs aren’t supposed to be able to write into it, given that it’s a system register and supposedly off-limits to EL0 programs.

But Martin discovered that userland code can write to just two individual bits inside this register – bits that are apparently otherwise unused and therefore might be considered unimportant or even irrelevant...

... and those bits can then be read out from any other userland program.

And that’s it!

That, in a nutshell, is the entirety of the “baked-in” security vulnerability CVE-2021-30747, also known as M1RACLES.
...
There’s nothing that you can do, but fortunately there’s nothing you need to do, so you can relax.

Clearly, if it is possible to access a register you're not supposed to have access to, it's a bug that must be fixed and I suppose it technically counts as a security vulnerability but does this really require creating an entire Internet domain and web site to advertise it?

Sounds like click-bait to me.